How long should a password actually be?
Length matters more than complexity: aim for at least 12 to 16 characters, and a passphrase of several random words is both stronger and easier to remember than a short string of symbols, because each extra character multiplies the number of guesses an attacker needs.
By Mubasher Hussain · Published 2026-02-11 · Updated 2026-10-08 · 1274 words · about 6 minute read
The short answer: at least 16 characters if you are choosing it yourself, and the maximum the site allows if a password manager is generating it. Everything else, the capital letter, the number, the exclamation mark, matters far less than the length, and some of it actively makes things worse.
Here is why, with the arithmetic rather than the folklore.
Entropy, in plain terms
Password strength is measured in bits of entropy. Each bit doubles the number of guesses an attacker needs. A password with 40 bits of entropy requires about a trillion guesses to exhaust; one with 80 bits requires about a trillion trillion.
For a randomly generated password, the calculation is simple: multiply the length by the log base two of the character pool size. Lowercase letters alone give 4.7 bits per character. Adding uppercase takes it to 5.7. Adding digits and symbols takes it to about 6.5.
| Password | Length | Pool | Entropy | Verdict |
|---|---|---|---|---|
Tr0ub4dor&3 | 11 | 95 | ~72 bits on paper | Far weaker in reality |
correcthorsebatterystaple | 25 | 26 | ~117 bits | Strong |
kR7#mQ9$vX2@pL5! | 16 | 95 | ~105 bits | Strong |
Password123! | 12 | 95 | ~79 bits on paper | Falls in seconds |
Look at rows one and four. Both score respectably by the raw formula and both are weak in practice. This is the crucial limitation of entropy maths: it only holds for passwords that were actually generated at random.
Why the formula lies about human-chosen passwords
Attackers do not brute-force blindly. They start with lists of passwords leaked from previous breaches, hundreds of millions of real passwords that real people actually chose. Then they apply transformation rules: capitalise the first letter, append a year, swap a for @, add an exclamation mark.
Password123! has 79 bits by the formula and appears near the top of every cracking dictionary in existence. It falls instantly. The formula is describing a search space the attacker never has to search.
Entropy maths is a valid measure of a randomly generated password and a poor measure of one a human invented. If you chose it yourself and it follows any recognisable pattern, assume it is substantially weaker than the number suggests.
What NIST actually recommends now
The US National Institute of Standards and Technology publishes the guidance that most organisations follow, and in Special Publication 800-63B it reversed several rules that had been standard for decades. The current advice is worth knowing because it contradicts what most websites still enforce:
- Require a minimum of 8 characters, and permit at least 64.
- Allow all printable characters, including spaces and emoji.
- Do not impose composition rules. No mandatory uppercase, digits or symbols.
- Do not force periodic expiry. Only require a change on evidence of compromise.
- Check new passwords against breach lists and reject known-compromised ones.
The reasoning behind dropping composition rules is that they produce predictable output. Told to add a capital and a number, the overwhelming majority of people capitalise the first letter and append a 1. The rule adds almost no real entropy while making the password harder to remember, which pushes people toward reuse, the single most damaging behaviour of all.
Forced 90-day rotation was dropped for the same reason. It reliably produces Spring2026 followed by Summer2026, which is worse than a strong password kept indefinitely.
Passphrases: the honest recommendation
Four or five random words are easier to remember than a string of symbols and mathematically stronger than most of them. Drawing randomly from a 7,776-word list, the standard Diceware list, gives 12.9 bits per word. Five words is 64 bits; six words is 77.
The critical word is random. Words you chose because they mean something to you are not random, and a passphrase built from a memorable phrase is dramatically weaker than one built from dice rolls. Let a generator pick them.
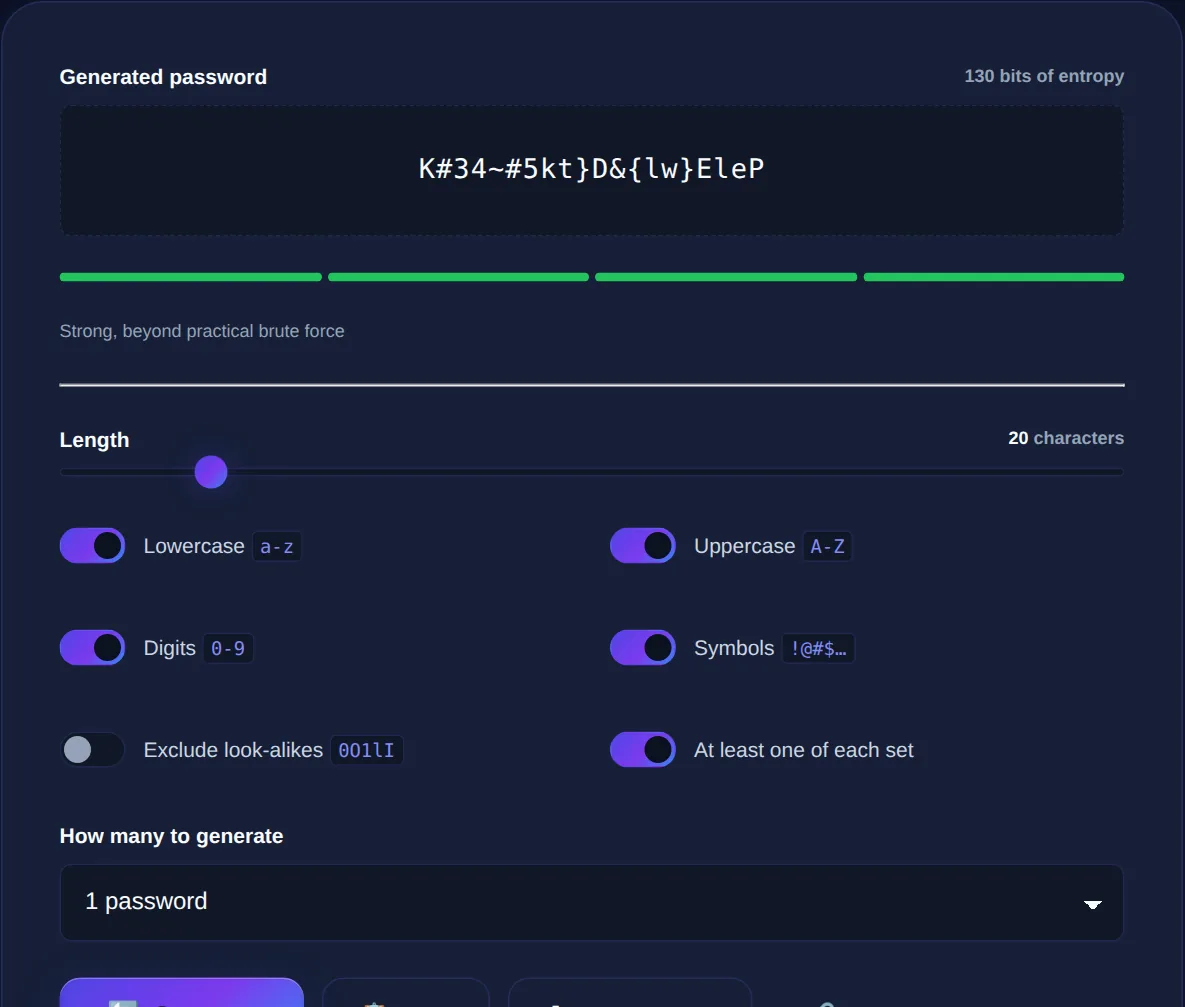
Generates passwords using crypto.getRandomValues(), the browser's cryptographically secure generator, not Math.random(), with rejection sampling to remove modulo bias. Nothing is transmitted; you can verify that in the Network tab.
How long would mine take to crack?
This depends far more on how the site stored your password than on the password itself, which is an uncomfortable thing to realise. Assuming a database has leaked and the attacker is working offline:
| Storage method | Guesses per second (one GPU) | 16-char random password |
|---|---|---|
| Unsalted MD5 | ~100 billion | Still centuries |
| SHA-256 | ~10 billion | Effectively forever |
| bcrypt (cost 12) | ~20 thousand | Effectively forever |
| Argon2id (tuned) | ~2 thousand | Effectively forever |
A genuinely random 16-character password is beyond reach under any of these. The reason the storage method still matters enormously is that most people's passwords are not random, and against a weak human-chosen password, the difference between SHA-256 and bcrypt is the difference between cracked in minutes and never cracked.
What matters more than length
Three things beat password length, and it is worth being blunt about them:
- Uniqueness. A perfect password used on two sites is only as safe as the less careful of the two. Credential stuffing, trying leaked pairs across other services, is the most common account takeover method there is.
- Two-factor authentication. An app-based or hardware second factor defeats credential stuffing entirely, even with a compromised password. This is the single highest-value thing most people can enable.
- A password manager. It makes uniqueness free. You stop needing to remember anything except one strong master passphrase, and every other password can be 30 random characters you never see.
If you do one thing after reading this, make it enabling two-factor authentication on your email account. Email is the reset path for everything else you own.
Scores entropy in bits, estimates offline crack time across four attacker capabilities, and flags the patterns that make a password weaker than its raw score suggests, dictionary words, keyboard runs, leetspeak substitutions and the word-plus-digits pattern.
Where passkeys fit in
The most significant recent change is not a longer password at all, it is not having a password. A passkey replaces the shared secret with a pair of cryptographic keys: a private key that never leaves your device and a public key the site stores. When you sign in, your device proves it holds the private key without ever transmitting it, so there is nothing for a breach to leak and nothing for a phishing page to capture. For any account that offers a passkey, it is stronger than even a long random password, because it removes the two weakest links at once, reuse and phishing.
Passwords are not going away yet, though. Many sites still do not support passkeys, account recovery often falls back to a password or an email link, and you still need a strong master passphrase to protect the password manager that holds everything else. So the practical position is simple: use a passkey wherever one is offered, and where it is not, use a long unique password from a manager with two-factor authentication on top.
So, a number
For a password you have to type and remember: a 5-word random passphrase, which is around 25 characters and 64 bits. For anything a password manager handles: whatever maximum the site permits, since you will never type it.
And if a site refuses a password because it is "too long" or rejects a space, that tells you something about the rest of its security engineering. It is a reasonable signal to use a unique password there and enable two-factor authentication if it is offered.